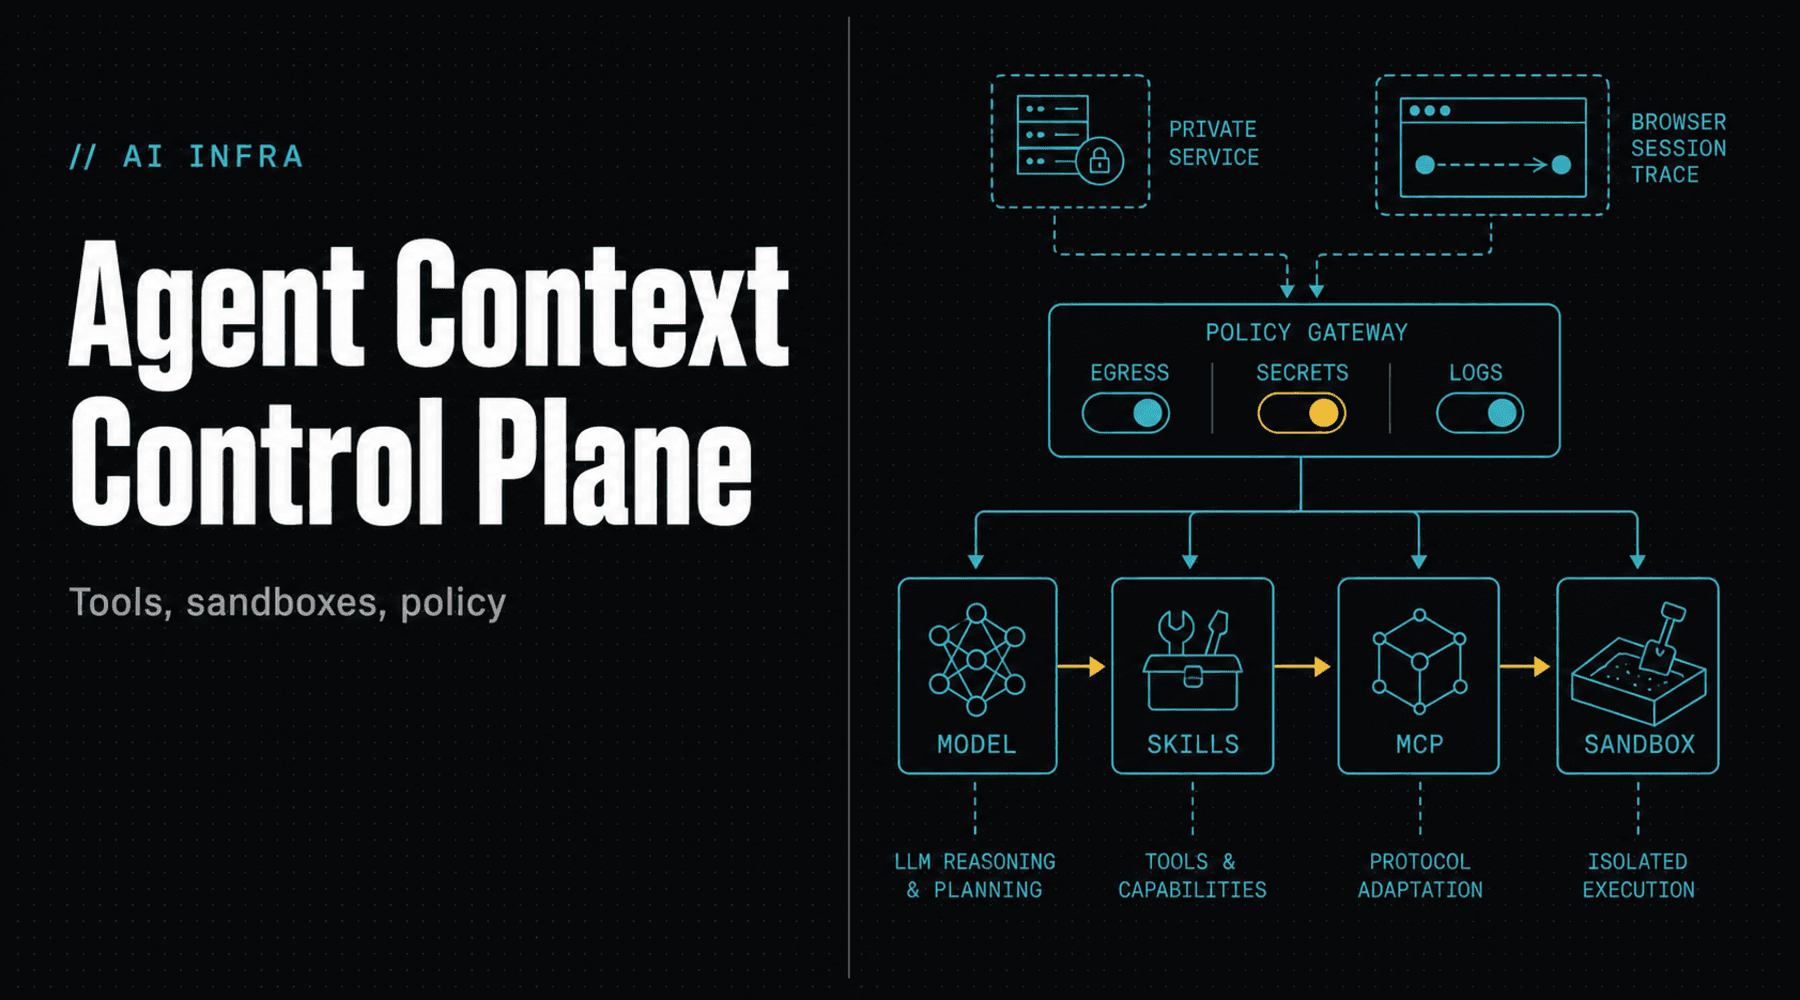
Agents Need a Context Control Plane
The next useful layer for AI agents is not another prompt trick. It is infrastructure that decides which tools, skills, sandboxes, private services, logs, and secrets an agent can touch.
// Archive
Pieces filed under Developer Tools.
Browse
The next useful layer for AI agents is not another prompt trick. It is infrastructure that decides which tools, skills, sandboxes, private services, logs, and secrets an agent can touch.
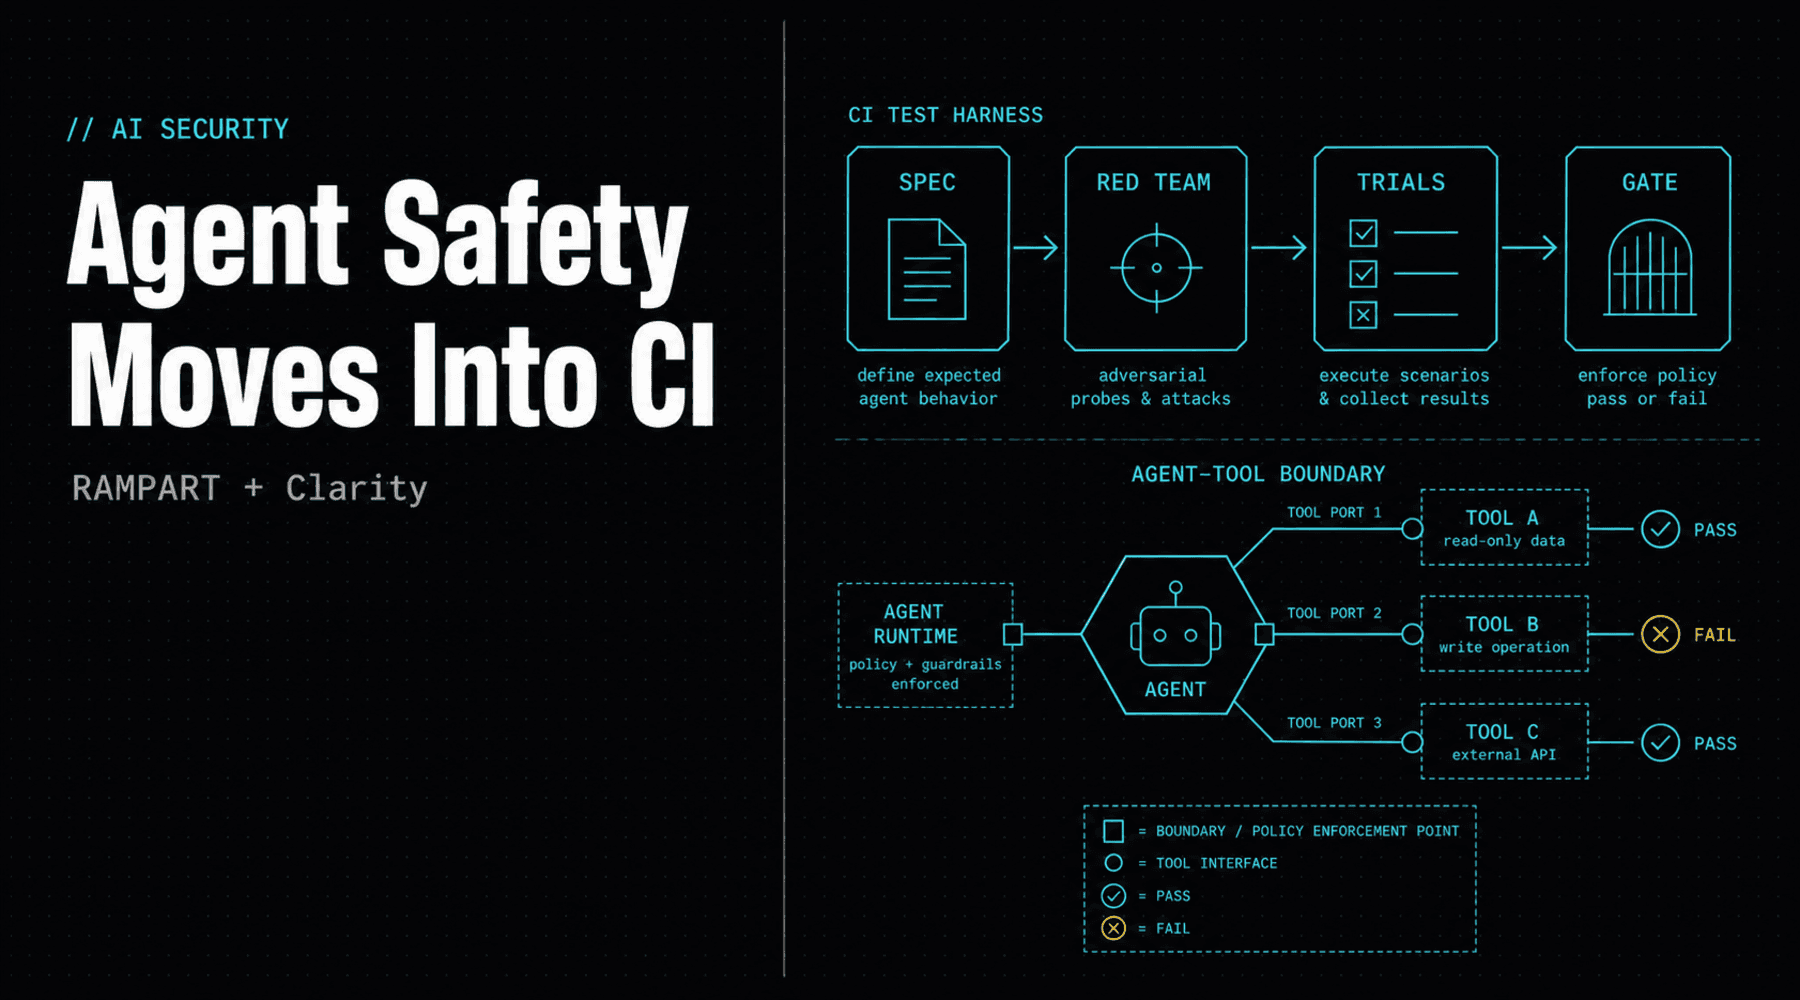
Microsoft's new open-source RAMPART and Clarity tools point agent safety toward the same place reliable software already lives: repeatable tests, design review, and CI gates.
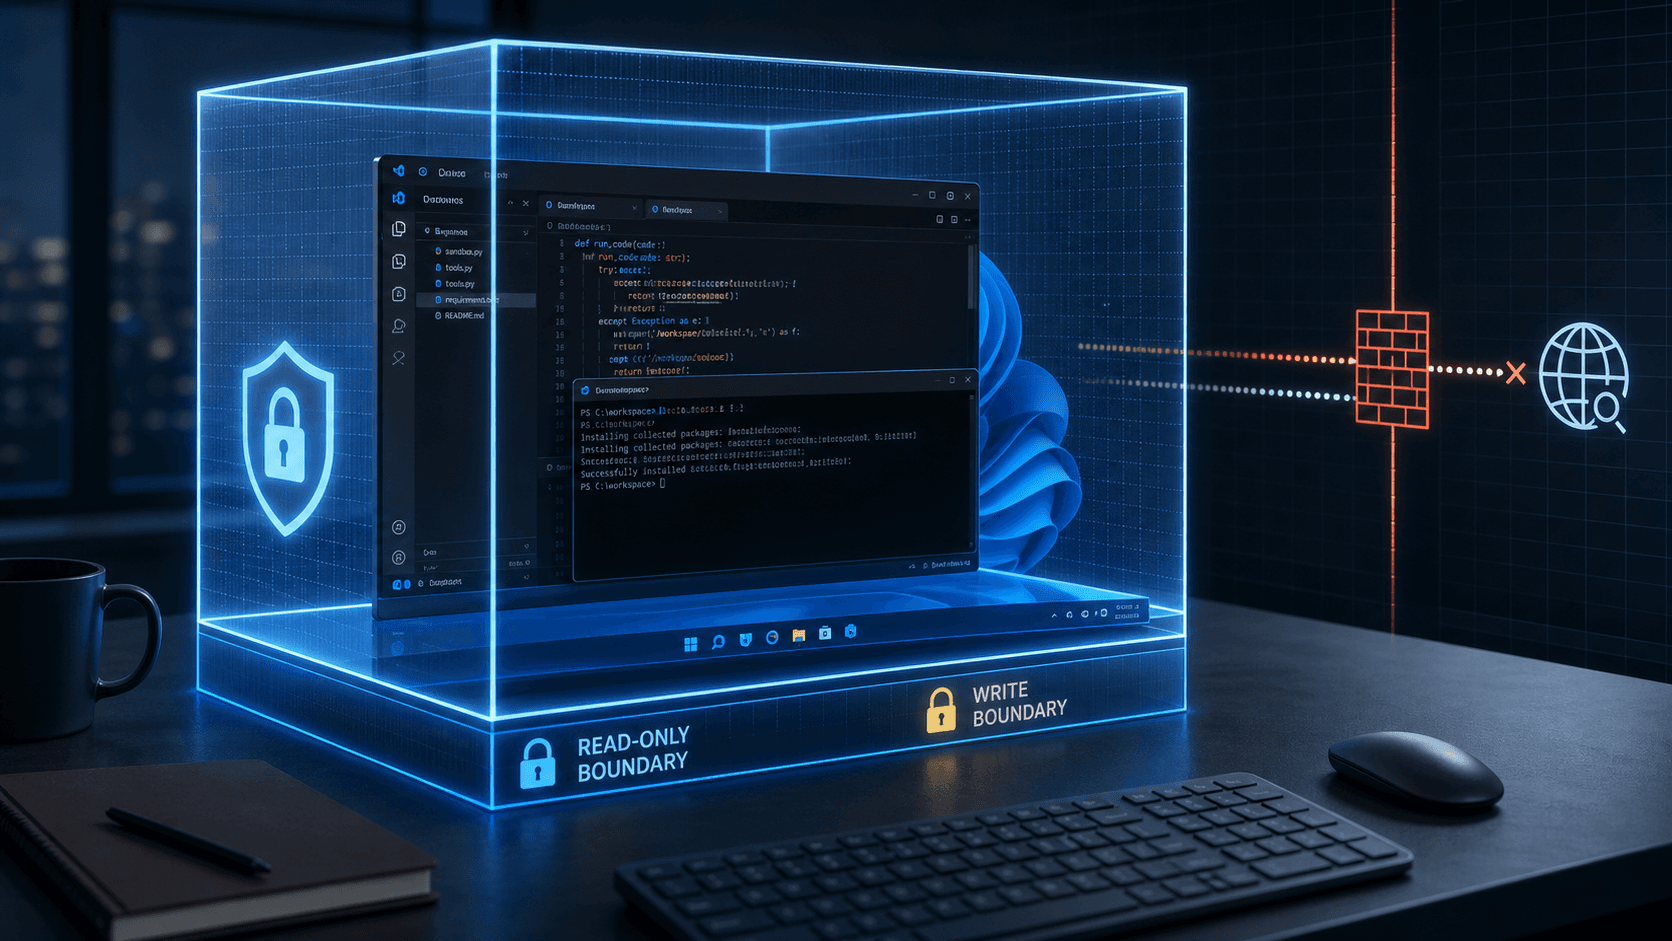
OpenAI's new Windows sandbox work for Codex shows that useful coding agents cannot live on vague trust. They need operating-system boundaries that match real developer workflows.
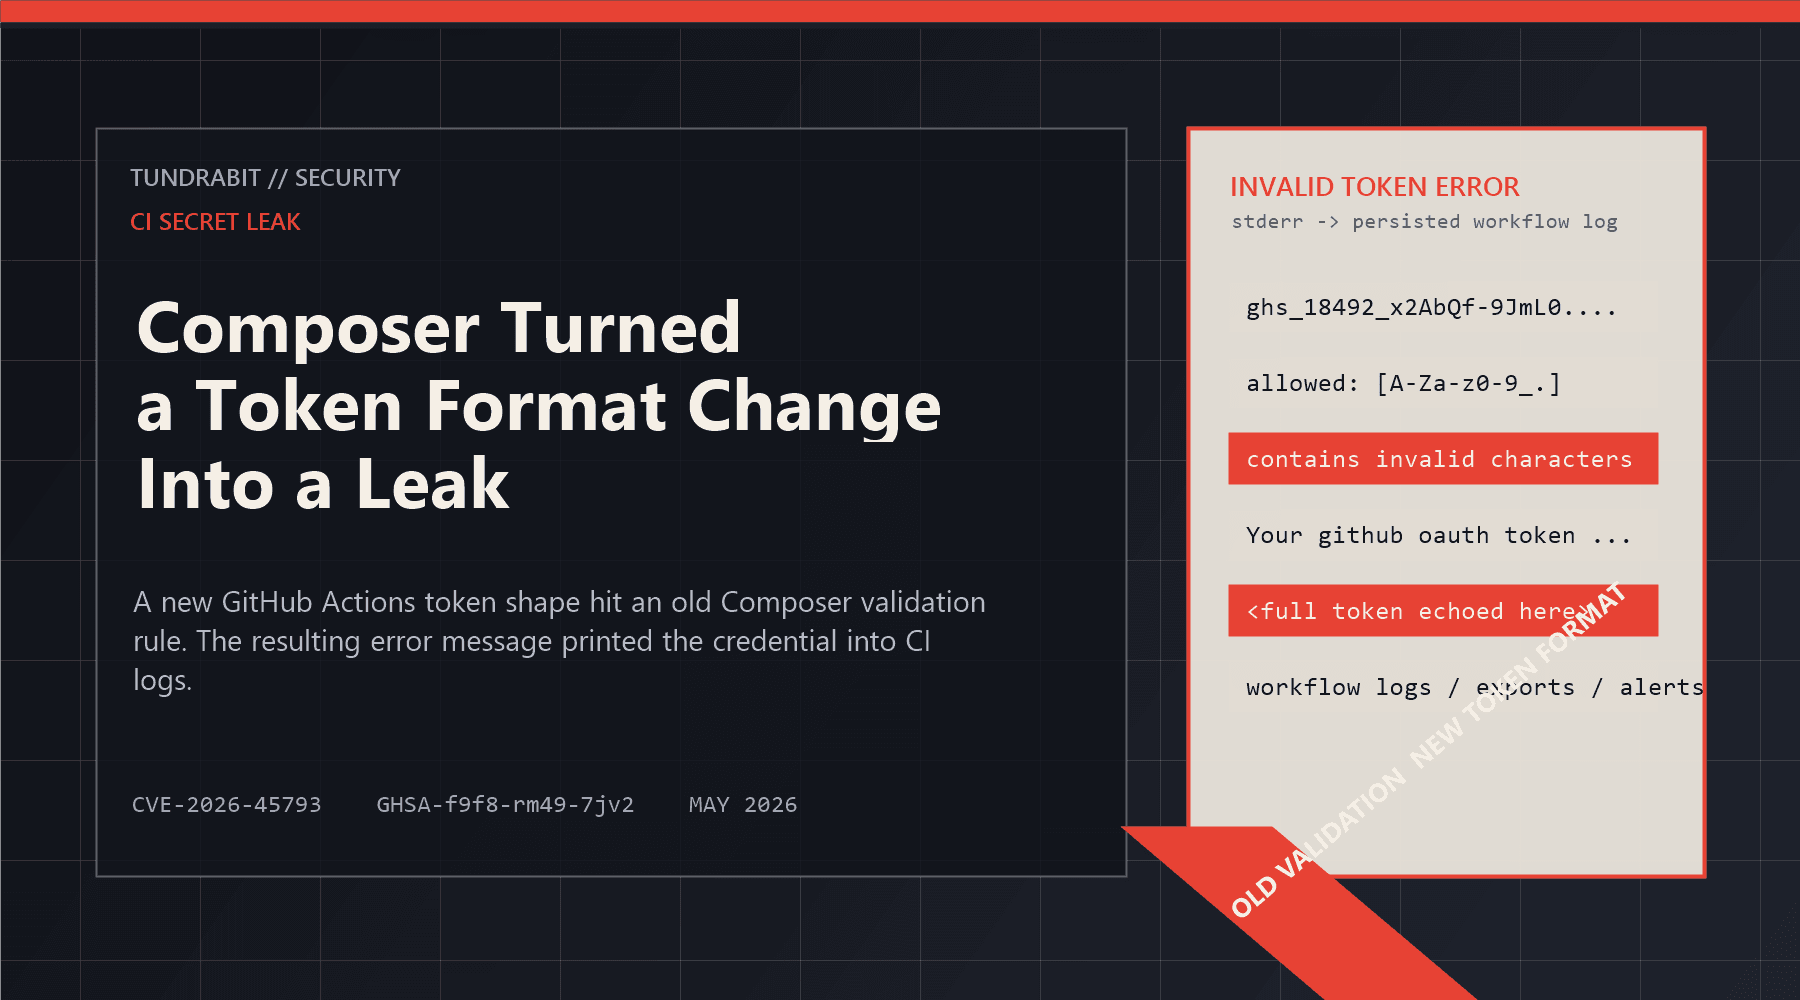
A small GitHub token format change exposed a brittle security assumption in Composer and turned ordinary GitHub Actions logs into a credential leak path for PHP teams.
GitHub's new generally available MCP secret scanning turns credential leaks into a live coding-time problem instead of a post-commit cleanup job. That is exactly where AI agents need security guardrails.